
Achieve ISO 27001 Certification
in Record Time
Implementation Made Effortless
Everything you need to build a robust ISMS, designed specifically for internal teams rather than expensive external auditors.
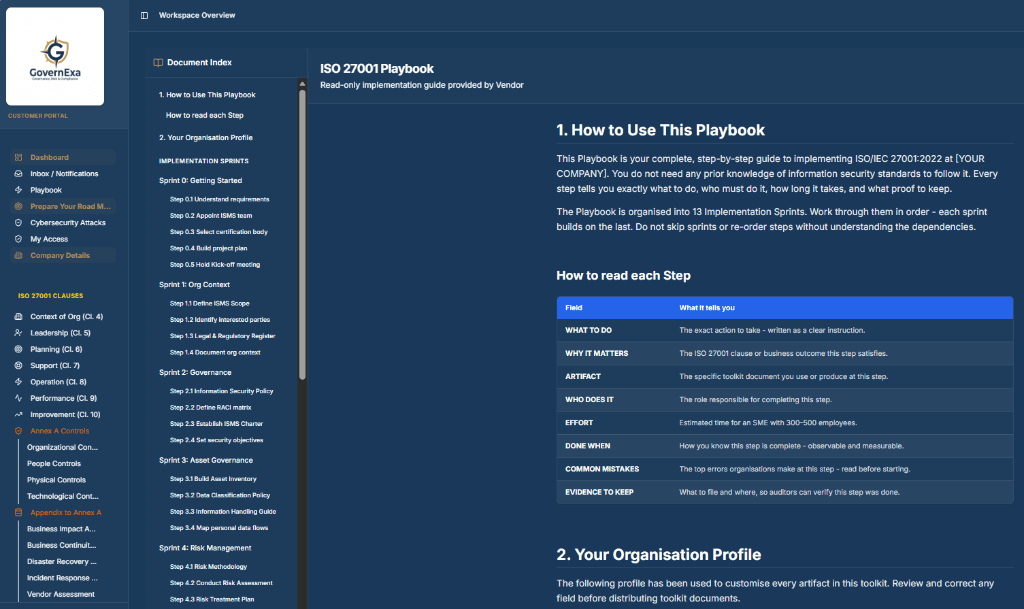
Step-by-Step Playbook
Our guided playbook translates complex ISO 27001:2022 clauses into actionable, everyday tasks that anyone on your team can understand and execute.
Empower Your Team
GovernExa is built to be intuitive, empowering your workforce and partners to take ownership of security compliance efficiently.
Audit-Ready by Design
Generate the exact reports, registers, and evidence that ISO auditors look for. Walk into your Stage 1 and Stage 2 audits with absolute confidence.
Comprehensive Built-in Modules
Everything you need, right out of the box.
The Ultimate Playbook for ISO 27001:2022
We've distilled thousands of pages of ISO standards into a streamlined, digital workflow. GovernExa tracks your progress from Day 1 to Certification.
Define the Context
Map your internal & external issues, interested parties, and ISMS scope instantly.
Risk Management
Built-in Risk Register to identify, assess, and treat risks with automated scoring.
Annex A Controls
Implement the 93 controls from the 2022 update with pre-built templates and checklists.
Continuous Improvement
Track non-conformities, corrective actions, and internal audits in one unified hub.
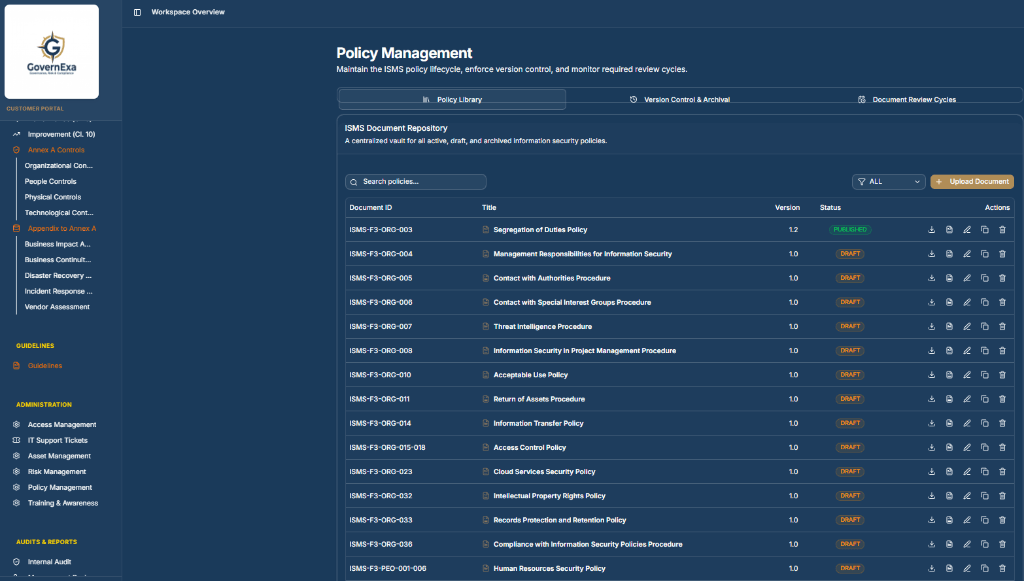
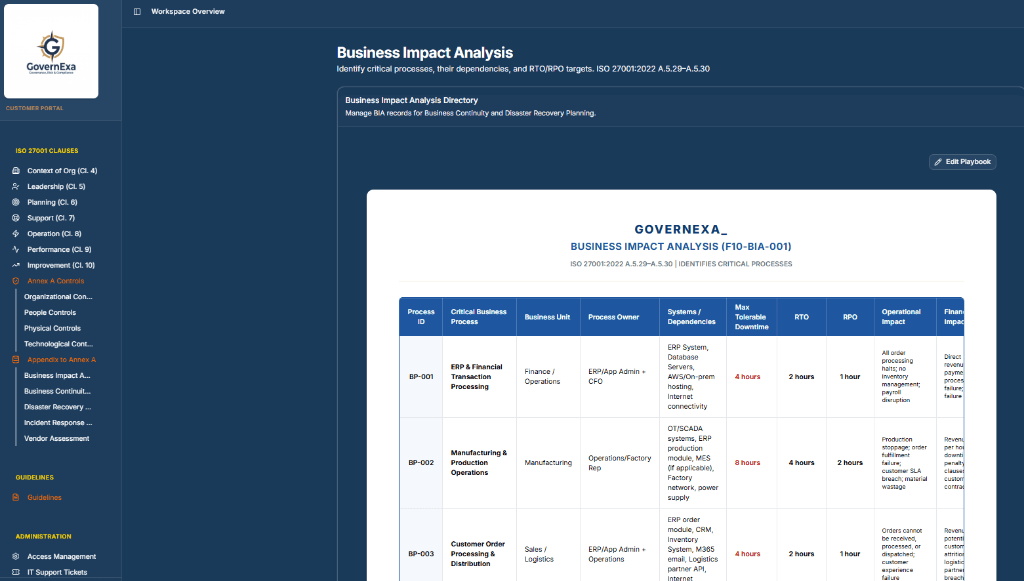
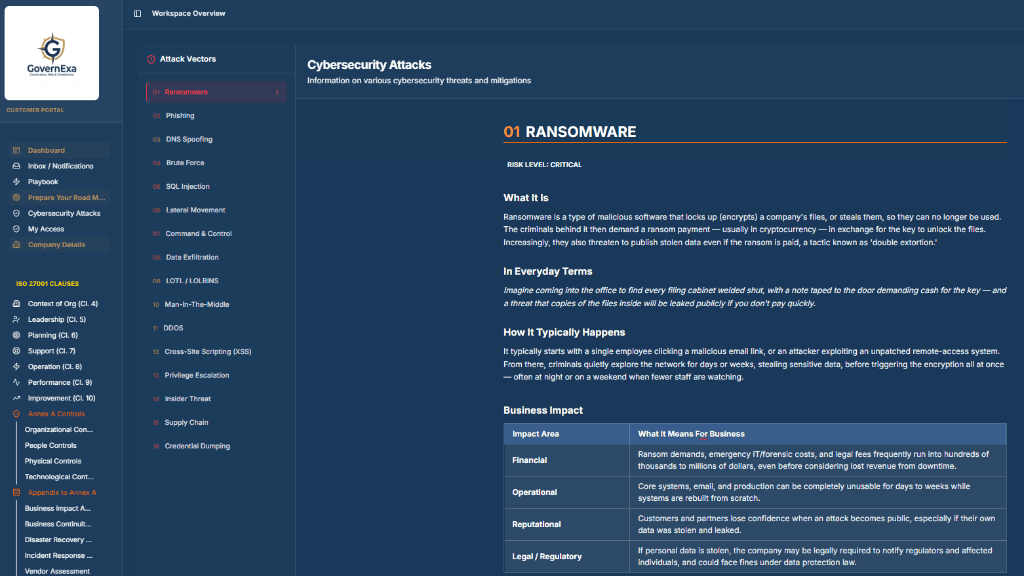
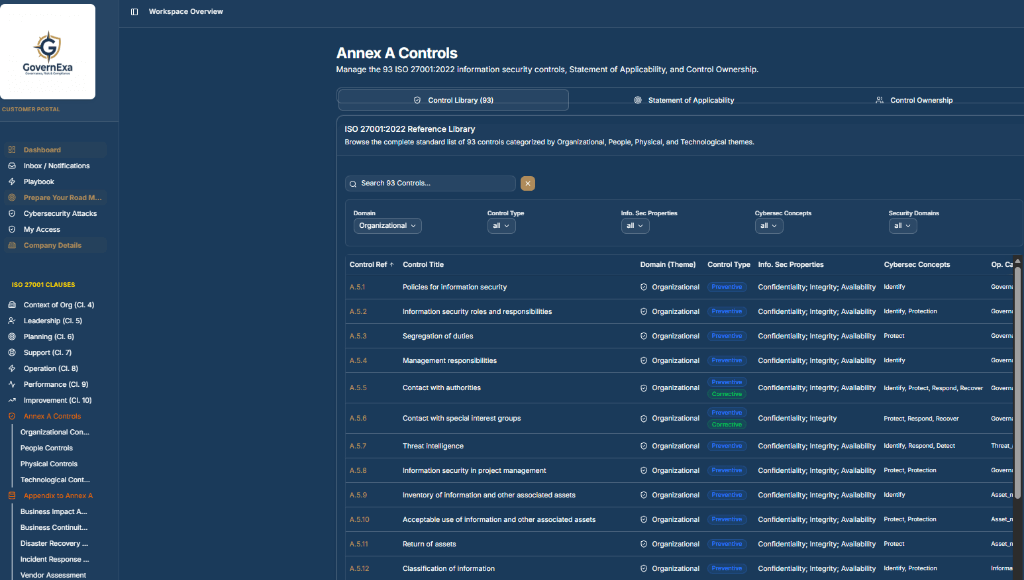
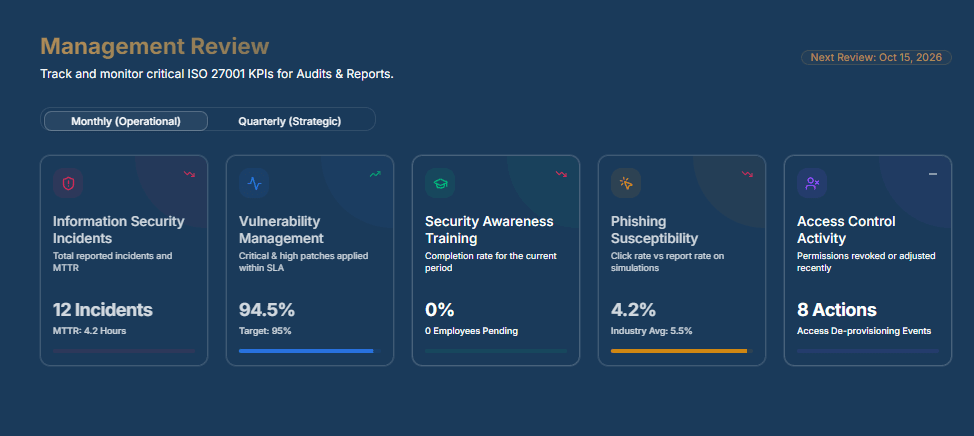
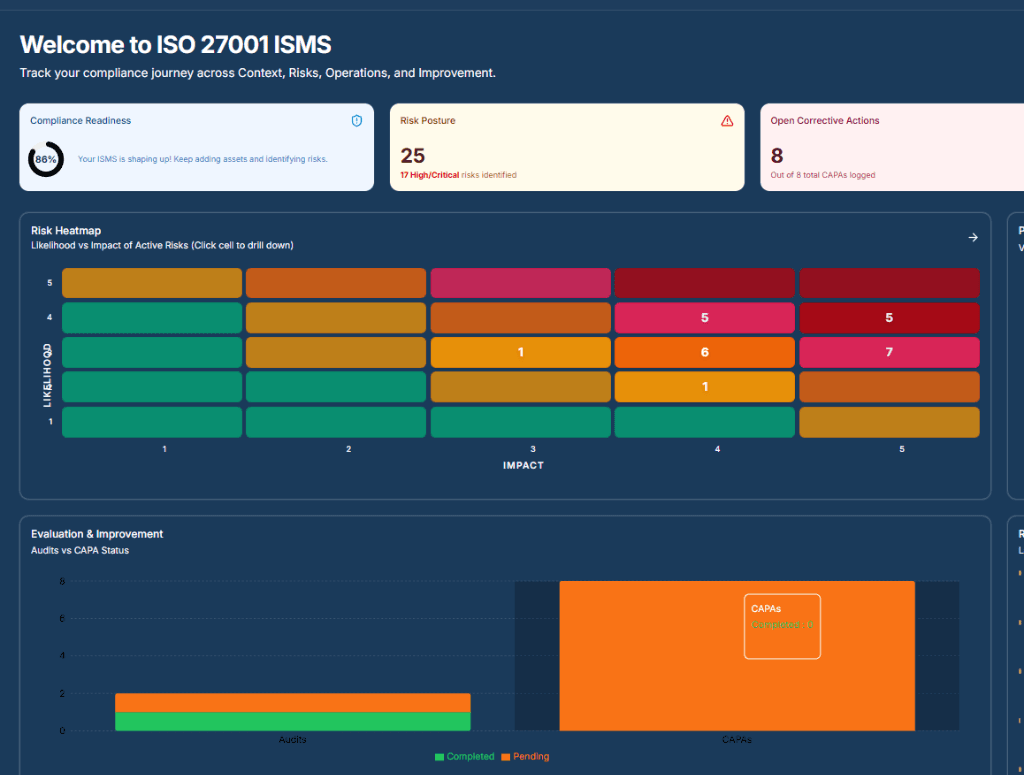
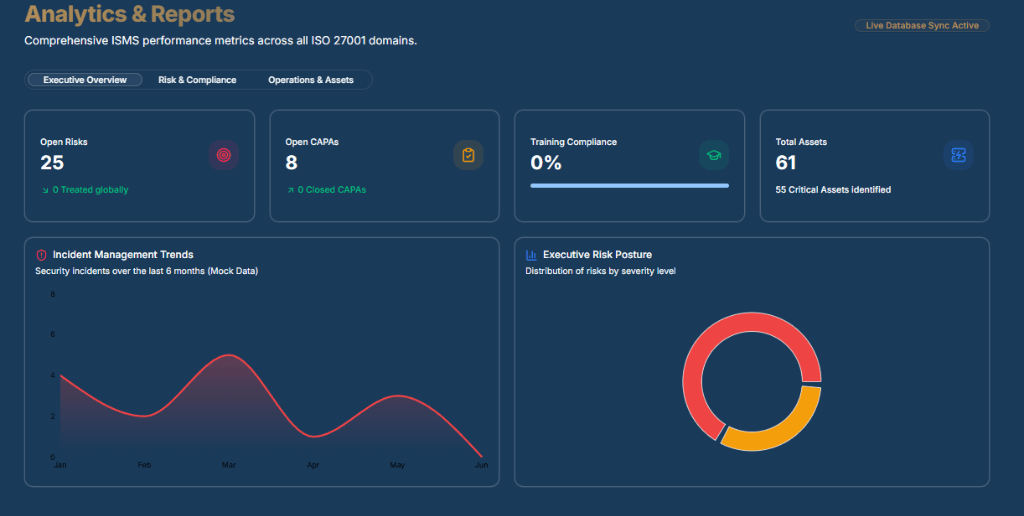
Real-time Dashboards & Reporting
Keep your finger on the pulse of your ISMS. GovernExa automatically aggregates data from across your organization into beautiful, executive-ready management reports.
Executive Overviews
Instantly see your overall compliance readiness, open risks, and CAPA status.
Risk & Compliance Metrics
Track incident trends, vulnerability SLA adherence, and phishing susceptibility.
Automated Management Reviews
Generate comprehensive reports for your mandatory management review meetings with one click.
Unmatched Benefits
Our ISO 27001 implementation platform delivers tailored, secure, and comprehensive governance for any organization, in any sector.
Universal Applicability
Designed for everyone. All industries can seamlessly implement ISO 27001 using our framework.
Highly Customizable
Fully customizable workflows, policies, and controls tailored precisely to your industry requirements.
Regulatory Governance
Meet strict governance standards for SEBI, RBI, Exchanges, RI's, Banks & Financial Institutions, Manufacturing, Exports, Pharmaceutical, Healthcare, and Engineering.
For Any Company Size
Implementation can be done for any size of the company whether SME, MSME, Large Corporate, etc.
Gap Assessments
Conduct comprehensive Gap Assessments directly within the platform to identify and remediate missing controls.
Consultant Friendly
Consultants can leverage GovernExa to drive implementations and organize documentation seamlessly with their clients.
Secure Data Sharing
Safely share compliance data and evidence with third parties or auditors without ever losing control of your sensitive data.